2 Public cloud images #
SUSE offers a variety of different product images for different use cases in partner cloud provider frameworks. Learn how to find the image that meets your use case.
2.1 Image lifecycle #
All SUSE public cloud images follow a refresh cycle up to the point of deletion. The refresh cycle follows a 'rolling' three month time frame. What this means:
Images in
activeandinactivestates are refreshed every three months. Replaced images are moved to thedeprecatedstate.If a critical security vulnerability occurs, images in
activeandinactivestates are updated as soon as possible once the fix for the affected code is available. For images inactiveandinactivestates the three month timer restarts with this forced replacement.SUSE is committed to address all security vulnerabilities disclosed through the
Common Vulnerabilities and Exposures process(CVE) and a score of 9.0 or greater in theCommon Vulnerability Scoring System(CVSS). For more information about the effects and rating of CVEs, refer to the SUSE CVE database.
The life cycle of an image consists of four different states:
- Active
Active images are fully supported and refreshed at least every three months. The duration lasts until the image is replaced by a newer image version.
- Inactive
Inactive images are supported following the rules of LTS(S) or ESPOS and will get refreshed at least every three months. The duration term is defined by the product. For more information, refer to https://www.suse.com/de-de/support/policy-products/#cloud
- Deprecated
Deprecated images may no longer be supported. The status of support depends on the support status of the product in the image. Deprecated images do not get refreshed and are not made available in regions added after an image has been set to
deprecated. At the end of the six month deprecation period, images are subject to deletion. It is strongly discouraged to use deprecated images to create new instances.- Deleted
Deleted images are no longer supported or available for instance creation.

active images for new instances
It is strongly recommended to only use active images to
launch instances for new deployments.
2.2 Naming scheme #
Names for SUSE's public cloud images consist of multiple parts that contain information about the product, its version, a time stamp indicating the release date of the image, and more. The general naming scheme for SUSE's public cloud images is as follows:
PRODUCT-FLAVOR-vVERSION-VIRTUALIZATION-STORAGE-ARCHITECTURE-TAXID-GEN
Not all components of this naming scheme are used in all frameworks.
PRODUCTAbbreviated name of the product in lower case letters, e.g.
suse-sles-15-sp3orsuse-manager-4-1-proxy. This part may also be “search-optimized” per cloud framework. For example the prefixsuse-helps when searching for SUSE in the general catalog in Amazon Web Services.FLAVORImages can have different flavors such as
chostorbyos. If it is the default image of a product, this part will be omitted. MultipleFLAVORattributes may be combined in an image name. For examplesles-15-sp3-chost-byosis an image build based on SUSE Linux Enterprise Server 15 SP3 build as a container host using a BYOS (Bring Your Own Subscription) billing model. Images withoutbyosin the name are set up the image is set up for PAYG (Pay As You Go) billing. For more information about the different billing models, refer to Section 1.3, “Plans”.SUSE Linux Enterprise flavors #basic(Azure-only)PAYG image that only includes updates but is not eligible for support (see Section 1.4, “Support”) or LTS(S) (see Section 3.3, “Enabling LTSS”).
byosBring your own subscription (BYOS) image
chostMinimal container host image
ecs(AWS-only)Amazon Elastic Container Service image
hardenedPre-hardened images, see Section 2.6, “Hardened Images”
hpcSUSE Linux Enterprise High Performance Computing image
sapSUSE Linux Enterprise Server for SAP applications image
sapcalSAP Cloud Application Library image
VERSIONUpload date of the image in the format
vYYYYMMDD(ISO 8601).VIRTUALIZATION(AWS-only)SUSE no longer supports or publishes para-virtualized images. The virtualization type was encoded as
pv(para-virtualized) orhvm(hardware-assisted virtual machine). Thehvmpart of the image name has been retained in an effort to not break backward compatibility.STORAGE(AWS-only)SUSE no longer publishes images that are based on hard disk (magnetic) backed storage. This used to be encoded as
mag. All published images are backed by SSD. Thessdpart of the image name has been retained in an effort to not break backward compatibility.ARCHITECTUREEither
x86_64orarm64. SUSE no longer supports or publishes 32 bitx86images. Images with thei386identifier are visible in Public Cloud Information Tracker data.TAXIDEither
llcorltd. Only for images with SUSE priority support. For more information, refer to Section 1.4, “Support”GENERATION(Microsoft Azure-only)appended as
gen2for 2nd Generation VMs.
2.3 Public Cloud Information Tracker #
The Public Cloud Information Tracker (PINT) provides information about the images SUSE publishes
and servers that are part of the SUSE operated update infrastructure.
PINT is available at https://pint.suse.com/ and provided as an API
and command-line tool with the python3-susepubliccloudinfo
package from the Public Cloud Module repository.
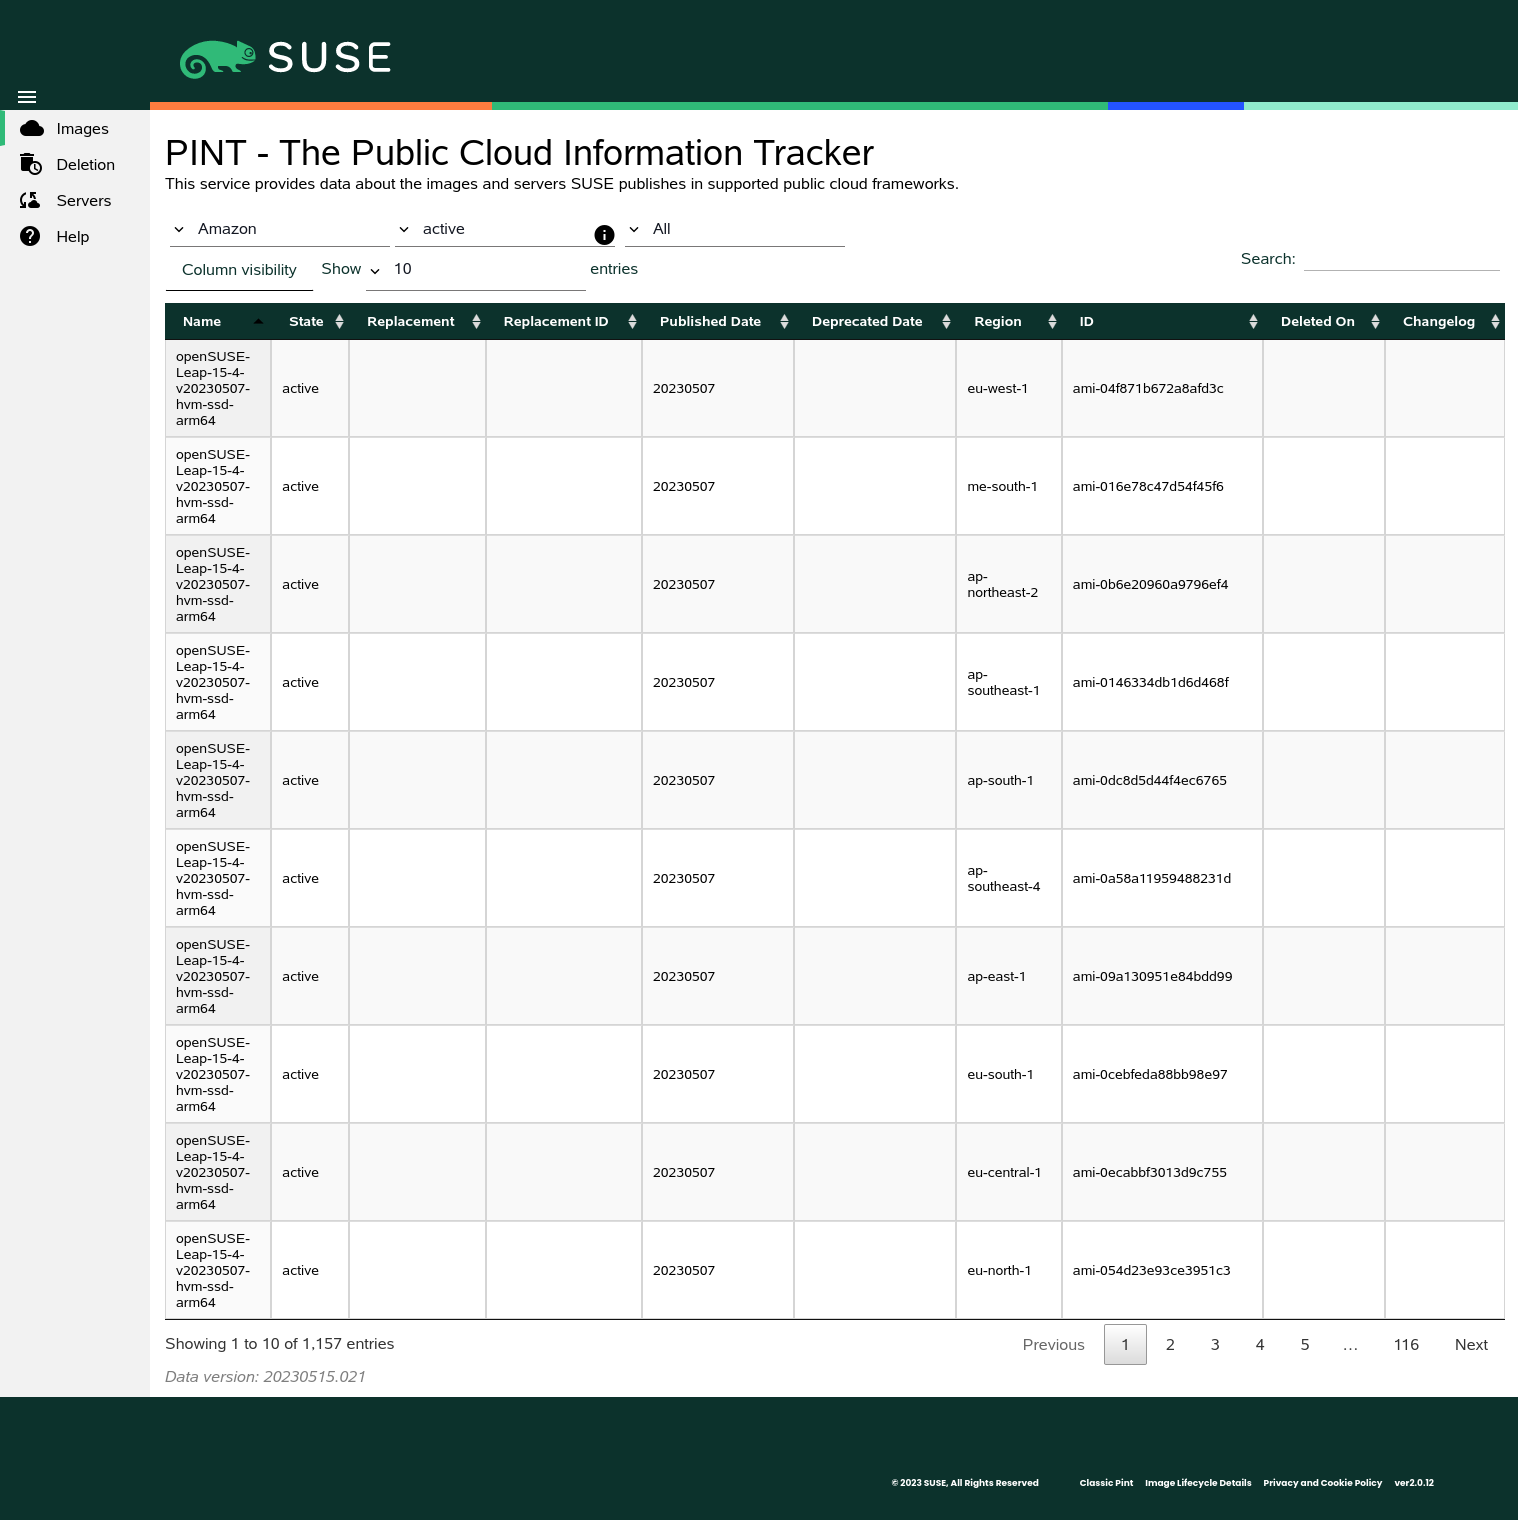
Use the drop-down lists to view images, servers, or both, and filter by cloud framework, region, or image state. You can also search for strings and adjust the columns and the number of results per page.
2.3.1 Images view #
The following columns are shown in the Images view. Some columns depend on
the the cloud frameworks.
Images view #- Name
Name of the image. For more information about the image naming scheme, refer to Section 2.2, “Naming scheme”.
- State
State of the image. Can be one of
All states,active,inactive,deprecated, ordeleted. Note thatAll Statesexcludes images in thedeletedstate. Deleted images may be viewed by explicitly selectingdeletedas the image state. For more information information about image stated, refer to Section 2.1, “Image lifecycle”.- Replacement
Name of the image that replaces another.
- Replacement ID
ID of the image that replaces another. Only shown for Amazon, and Alibaba; images on Google and Microsoft do not have IDs.
- Published Date
Publication date of the image. Displayed in the format
YYYYMMDD(ISO 8601).- Deprecated Date
Date the image was deprecated by a newer one. Displayed in the format
YYYYMMDD(ISO 8601). Only shown for deprecated or deleted images.- Project
Project of the image. Projects are used to organize Google Cloud Platform resources. Only shown for Google Cloud Platform.
- Region
Region of the image.
- Environment
Environment of the image. Only shown for Microsoft Azure.
- ID
Unique identifier of the image. While the
Nameof an image is the same across different regions, theIDis unique.- URN
Uniform Resource Name of an image. While the
Nameof an image is different across the environments, theURNis the same. Only shown for Microsoft Azure.- Deleted on
Date the image was deleted in the format
YYYYMMDD(ISO 8601). Only shown for deleted images.- Changelog
Link to a detailed changelog with a software bill of materials (SBOM), CVE list and a detailed vulnerability scan report. If the image replaces a previous image of the same product version, additional information such as image configuration changes, package version changes and package changelogs are also available. For more information, refer to Section 2.4, “Change information”
2.3.2 Servers view #
The following columns are shown in the Servers view:
Servers view #- Name
Host name of the server. Region servers do not have host names. Host names are not DNS resolvable.
- IP
IP address of the server.
- Region
Region of the server. For optimal performance SUSE provides servers in most regions of a cloud framework.
- Type
One of
regionserver-sles,regionserver-sap, orsmt. In every framework where SUSE operates an update infrastructure, theregionserversystems are randomly distributed across regions and thesmtservers are available in most regions. Every region hasupdateservers assigned.
2.4 Change information #
Image change information is divided into different categories:
Image Configuration Changes(only for updated images)This category describes changes in the image setup; for example, if a new service was enabled, kernel parameters were changed, or if packages were added or removed.
Vulnerability fixes(only for updated images)This category lists security fixes in the image. Entries are cross linked to the SUSE CVE database. For more information, refer to Section 2.1, “Image lifecycle”.
Package List(only for initial images)This category lists all packages and their versions in the image.
Package Version Changes(only for updated images)This category lists all packages that had version changes compared to the previous image and the version in that image.
Package Change Logs(only for updated images)This category shows a concatenated changelog of all packages that had changes compared to the previous image and the version in that image.
Software bill of materials (SPDX)This category shows an SBOM in the
Software Package Data Exchangeformat.SPDXis an open standard backed by the Linux Foundation. For more information, refer to https://spdx.dev/.Software bill of materials (CycloneDX)This category shows an SBOM in the
CycloneDXformat. This format is backed by the Open Worldwide Application Security Project (OWASP) foundation. For more information, refer to https://cyclonedx.org/.Vulnerability report(only for updated images)This category provides a detailed vulnerability scan report performed at image publication time. Fixed CVEs are listed by their CVSS3 scores along with descriptions and the affected packages.

Naturally, the information for the initial image of a specific product version is limited as there is no earlier image for comparison. For more information about the new product version, refer to the product's release notes at https://www.suse.com/releasenotes.
To allow for automatic retrieval of image change information, all URLs follow the schema:
https://publiccloudimagechangeinfo.suse.com/FRAMEWORK/IMAGE/CHANGES.html
FRAMEWORK is the cloud framework as used in the
pintcommand-line tool; i.e. one ofalibaba,amazon,google, ormicrosoft.IMAGE is the name of the image as shown by PINT, e.g.
suse-sles-15-sp3-byos-v20220127-hvm-ssd-x86_64.CHANGES is the category of the changes, i. e. one of
cve_fixes,image_changes,package_changelogs, orpackage_version_changes. Do not forget the.htmlextension to complete the URL.
2.5 Image content #
The content of the SUSE-published images may change between image updates. Any changes are captured in the published changelog (Section 2.4, “Change information”). The content of the images consists of basic utilities and applications considered generally useful or used often. If you have specific package requirements, please ensure that the packages required for your purposes get installed or remove packages you may not need.
SUSE Linux Enterprise Server and SUSE Linux Enterprise Server-basic images in Microsoft Azure contain the
kernel-azure flavor build. This kernel does not receive
LTS(S) support and therefore will get replaced by
kernel-default upon image refresh when the distribution
enters the LTS(S) period and the image changes state to
inactive. The kernel-azure flavor
does not have the same kABI (kernel Application Binary Interface)
guarantees as the kernel-default, meaning the kABI of
kernel-azure may change within a given Service Pack (SP)
or minor release. kernel-azure is not supported for
SAP applications. If you need a stable kABI in your SUSE Linux Enterprise Server or
SUSE Linux Enterprise Server-basic instance, install kernel-default instead.
2.6 Hardened Images #
To improve overall security, SUSE provides hardened images of some
products. The images are hardened using OpenSCAP, a collection of open source tools that
implement the Security Content Automation
Protocol (SCAP).
For more information and instructions on how to harden instances with OpenSCAP, refer to Section 3.4, “Hardening instances”.
2.7 Google Sovereign Cloud Images #
This section describes how to create instances from a SUSE image file in Google Sovereign
Cloud. The procedure creates a storage bucket, uploads the image file, creates a compute image
from it and creates an instance. Except for the image creation step, these steps can be
performed with the Google Cloud Console or with gcloud. The procedure that follows
covers the relevant gcloud commands only.
Image creation requires gcloud. The Google Cloud Console cannot set the guest
operating system features that the image requires. All other steps can also be
performed in the Google Cloud Console. For more information about the guest operating system
features, see
https://docs.cloud.google.com/compute/docs/images/create-custom#guest-os-features.
Before you start, make sure that:
The
gcloudcommand-line tool is installed and authenticated. For more information about installing and setting upgcloud, see https://docs.cloud.google.com/sdk/docs/install-sdk. Note that authentication to the Google Sovereign Cloud region requires different credentials than the public Google Cloud Platform endpoint.You have a Google Sovereign Cloud project with the Compute Engine API enabled.
Your account has the permissions to create storage buckets, upload objects, create images and create instances in the project.
The commands in this section use the following placeholders. Replace them with your values:
- PROJECT_ID
The ID of your Google Sovereign Cloud project. Use the same project ID in all commands.
- LOCATION
The region or multi-region in which to create the bucket and store the image.
- BUCKET_NAME
The name of the storage bucket that holds the image file. The bucket name must be globally unique. Use the same bucket name in all commands.
To create instances from an image file, perform the following steps.
Create a storage bucket:
>gcloudstorage buckets create gs://BUCKET_NAME \ --project=PROJECT_ID \ --location=LOCATIONDownload the image file from the SUSE download site:
In a web browser, open https://suse.com/products/.
Click to log in with your SUSE account, or to create an account if you do not have one.
In the section, select the product whose image you want to use: SUSE Linux Enterprise Server or SUSE Linux Enterprise Server for SAP applications and click .
Select the release. Supported releases are and .
Select the architecture of your instance. Supported architectures are or . Images of SUSE Linux Enterprise Server for SAP applications are only available for .
In the list, find the Google Compute Engine image that matches the release, product and architecture. The image names use the following patterns:
SUSE Linux Enterprise Server 16.0:
SLES-16.0-BYOS.ARCHITECTURE-VERSION-GCE-SOV-Update-DATE.tar.gzSUSE Linux Enterprise Server 16.0, hardened:
SLES-16.0-Hardened-BYOS.ARCHITECTURE-VERSION-GCE-SOV-Update-DATE.tar.gzSUSE Linux Enterprise Server for SAP applications 16.0 (hardened by default):
SLES-SAP-16.0-BYOS.x86_64-VERSION-GCE-SOV-Update-DATE.tar.gzSUSE Linux Enterprise Server 15 SP7:
SLES15-SP7-BYOS.ARCHITECTURE-VERSION-GCE-SOV-Update-DATE.tar.gzSUSE Linux Enterprise Server 15 SP7, hardened:
SLES15-SP7-Hardened-BYOS.ARCHITECTURE-VERSION-GCE-SOV-Update-DATE.tar.gzSUSE Linux Enterprise Server for SAP applications 15 SP7:
SLES15-SP7-SAP-BYOS.x86_64-VERSION-GCE-SOV-Update-DATE.tar.gzSUSE Linux Enterprise Server for SAP applications 15 SP7, hardened:
SLES15-SP7-SAP-Hardened-BYOS.x86_64-VERSION-GCE-SOV-Update-DATE.tar.gz
In the file names, replace the placeholders as follows:
ARCHITECTURE is
x86_64for oraarch64for .VERSION is the version of the image.
DATE is the build date of the image in the format
YYYYMMDD.
Images with
Hardenedin the file name are hardened images. Images of SUSE Linux Enterprise Server for SAP applications 16.0 and later are hardened by default, so their file names do not containHardened. For more information about hardened images, see Section 2.6, “Hardened Images”.Click next to the image.
The following steps refer to the image file as
IMAGE_FILE.tar.gz.Upload the image file to the bucket:
>gcloudstorage cp IMAGE_FILE.tar.gz \ gs://BUCKET_NAME/ \ --project=PROJECT_IDCreate a compute image from the uploaded image file and set the guest operating system features. This is the only step that requires
gcloud. The command depends on the architecture of the image.For
x86_64images, run:>gcloudcompute images create IMAGE_NAME \ --source-uri=gs://BUCKET_NAME/IMAGE_FILE.tar.gz \ --guest-os-features=UEFI_COMPATIBLE,VIRTIO_SCSI_MULTIQUEUE,SEV_CAPABLE,\ SEV_LIVE_MIGRATABLE,SEV_LIVE_MIGRATABLE_V2,SEV_SNP_CAPABLE,TDX_CAPABLE,\ IDPF,GVNIC \ --storage-location=LOCATION \ --architecture=X86_64 \ --project=PROJECT_IDFor
aarch64images, run:>gcloudcompute images create IMAGE_NAME \ --source-uri=gs://BUCKET_NAME/IMAGE_FILE.tar.gz \ --guest-os-features=UEFI_COMPATIBLE,VIRTIO_SCSI_MULTIQUEUE,GVNIC,IDPF \ --storage-location=LOCATION \ --architecture=ARM64 \ --project=PROJECT_IDReplace IMAGE_NAME with a name for the new image.
For more information about the guest operating system features, see https://docs.cloud.google.com/compute/docs/images/create-custom#guest-os-features.
Create an instance of the image:
>gcloudcompute instances create INSTANCE_NAME \ --image=IMAGE_NAME \ --image-project=PROJECT_ID \ --project=PROJECT_ID \ --zone=ZONE \ --machine-type=MACHINE_TYPEReplace INSTANCE_NAME with a name for the instance and ZONE with the zone in which to create it. Replace MACHINE_TYPE with the machine type to use.
The
--projectoption sets the project in which the instance is created. The--image-projectoption sets the project that contains the image. If you share images across projects, the two values can differ.Verify that the instance is running:
>gcloudcompute instances list \ --project=PROJECT_ID(Optional) Log in to the instance:
>gcloudcompute ssh INSTANCE_NAME \ --project=PROJECT_ID \ --zone=ZONETo log in, the instance must be on a network that is accessible from your system. The instance needs an external IP address and a firewall rule that allows SSH traffic. If the instance has only an internal IP address, connect from a system within the same network, for example through a virtual private network (VPN) or a bastion host.
For more information about setting up the network, see https://docs.cloud.google.com/vpc/docs/vpc.
(Optional) After you create the image, you can delete the image file from the bucket to avoid storage costs:
>gcloudstorage rm \ gs://BUCKET_NAME/IMAGE_FILE.tar.gz \ --project=PROJECT_ID
For more information about registering the instance with the SUSE update infrastructure, see Section 3.1, “Registering instances”.